Run a phishing simulation for your employees yourself - in 15 minutes
Nothing to install, no technical knowledge needed*, no monthly or annual commitment. A one-time payment per campaign from ₪999, including a summary report and an awareness training certificate that supports part of the requirements of Amendment 13. Prefer that we run it for you? A full managed service is also available → · For partners: white label →
To order awareness training only (in person or remote) →
* Setting up the campaign takes less than 15 minutes and needs no technical knowledge. One simple action is required from the organization's IT team (allowlisting the sender). Launch is subject to a review and approval by the information security team, up to one business day.
First, check your exposure for free:
Free phishing exposure check
The check will reveal, for example, whether someone can send an impersonating email in your organization's name to your customers.
Can hackers easily send a phishing email to your employees?
DMARC • SPF • DKIM - instant results
yossi.cohen@phishingu.com
maya.bar@phishingu.com
avi.mizrahi@phishingu.com
noa.frid@phishingu.com
You have a new message waiting for you in Microsoft Teams from the HR department, including a document to approve by the end of the day.
For security reasons, the message can be viewed only after signing in again to your work account.
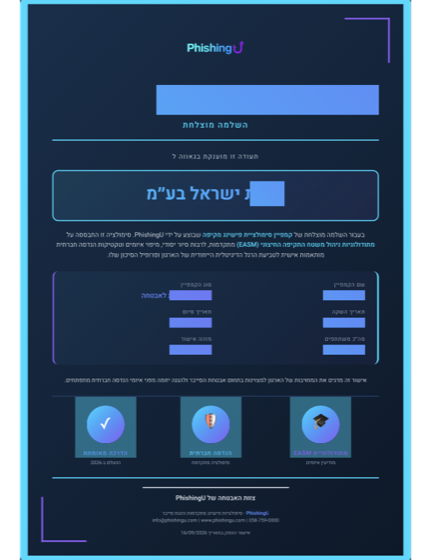
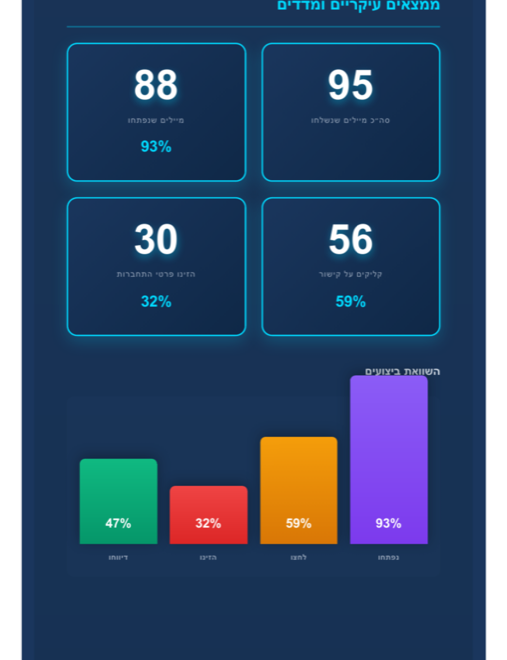
An initial check based on public DNS records. No commitment. Includes a practical recommendation for next steps.
What does PhishingU do?
The main service: PhishingU lets any organization run a phishing test for its employees as a self-serve service, in under 15 minutes* - nothing to install, no subscription and no commitment, from ₪999 per campaign. You build the campaign in the wizard, see an accurate preview of what the employee will receive, pay, and the system sends it. At the end you receive a summary report and an awareness training certificate.
An additional option - managed service: For those who prefer not to run anything on their own, we manage the process for you end to end: we check email impersonation exposure, plan a controlled phishing campaign, coordinate the technical aspects with your IT team, run the simulation, analyze the results and deliver a management report and in-person training for employees.
* Setting up the campaign takes less than 15 minutes and needs no technical knowledge. One simple action is required from the organization's IT team (allowlisting the sender). The actual launch of the campaign is subject to a review and approval by the information security team, a process that can take up to one business day.
- Identifying weak points and impersonation exposure using an EASM scan and artificial intelligence, including the status of SPF, DKIM and DMARC.
- Controlled phishing simulations for employees, departments or management.
- Social engineering scenarios: phishing, SMS phishing, vendor impersonation, urgent messages and spoofed links.
- Management reports with data, insights and recommendations.
- In-person training based on the results of your campaign, not on a generic video.
- A managed service, with no need for the customer to operate a system.
How it works - self-serve
Run a phishing simulation for your employees yourself, in under 15 minutes, with nothing to install and no commitment
Make the human factor your organization's first line of defense
Most cyberattacks begin with a human moment: an email that looks trustworthy, an urgent text message, a spoofed link or a request that looks legitimate. PhishingU tests your organization's exposure to impersonation, runs Controlled phishing simulations, and delivers in-person training that strengthens employees' ability to recognize, stop and report.
How it works - managed phishing campaign service
From an initial exposure check to a management report and in-person training - we lead the entire process for you
We check email impersonation exposure
Using an EASM system and artificial intelligence, we identify email impersonation exposures and weak points in your domain. The check is based on public DNS records, with no access to internal systems.
We scope a safe exercise
In a short scoping meeting we define together the target audience, departments, difficulty level, delivery method, exercise boundaries and the required IT approvals. One conversation is usually enough.
We run a controlled phishing simulation
We run a realistic but approved and controlled phishing campaign for you, without your organization having to operate a system itself. Technical coordination with IT is minimal and structured.
We analyze, report and train
At the end of the campaign you receive a detailed management report with data, insights and recommendations, ready for a management meeting and an employee session. We then deliver focused in-person training and a repeat exercise after an agreed period to measure effectiveness.
Don't want to run a system on your own?
We run the exercise for you.
Our main service is running a self-serve phishing test in under 15 minutes. But if you prefer not to run anything on your own, PhishingU also provides an end-to-end managed service as an additional option. we plan the exercise, coordinate the technical settings with your IT team, run the campaign, analyze the results and deliver a management report and in-person training for employees.
Prefer to run it yourself? Start with the self-serve service from ₪999 →

- No system to install on the customer's side
- No technical knowledge needed from management
- Only a short technical coordination with IT / information security
- A campaign tailored to employees, departments and language
- Detailed management reports, ready for a management meeting and an employee session
- In-person training available in Hebrew and English
- A quarterly or annual awareness program is available
A cyber company, consultant or MSP?
Offer your customers a phishing simulation under your own brand.
Do you manage many customers and want a managed solution without dedicating a team or running a dashboard? You give the instruction and we deliver: phishing simulations, reports and awareness training in your company's name (the scope of branding is agreed in advance).
Why does in-person training have more impact than a video?
Awareness videos are a good way to complement knowledge, but employees often watch them passively and do not change their actual behavior. In-person training allows conversation, questions, real examples from the campaign carried out in your organization, and an explanation tailored to employees' roles and risks.
"Instead of sending yet another generic video, we turn the campaign results into practical, in-person learning: what the employees saw, why it looked credible, what the warning signs were, and how to report correctly next time."
Advantages of in-person training
- Employees see examples that are close to what they actually received
- Common mistakes can be explained without blaming employees
- Questions can be answered in real time
- The training connects the simulation results with everyday behavior
- The impact is stronger when the training follows a real campaign carried out in your organization
- Especially suitable for organizations that want to improve a reporting culture and not just tick "training completed"
A controlled and approved simulation
A good phishing exercise is not meant to embarrass employees or to "catch" them. The goal is to identify awareness gaps, improve reporting, strengthen information security habits, and give management a true picture of the organization's phishing risk.
Start with an email impersonation exposure check - free of charge
We will scan your domain using an EASM system and artificial intelligence, identify weak points and impersonation exposures, and build a phishing exercise for you based on the findings, including training and a repeat exercise after a pre-agreed period.
What you get in the initial check
- An EASM and artificial intelligence scan to identify weak points
- A check of SPF, DKIM and DMARC - the state of your domain settings
- An initial indication of email impersonation risk
- A phishing exercise built from the findings
- A recommendation for a phishing simulation + training + repeat exercise
- An option for a short scoping meeting
- An offer of in-person training for employees
Services and information pages
Ready to check your domain's exposure?
After a short scoping call, we will build a controlled phishing campaign, a management report and focused employee training for you.
A practical service for organizations, information security consultants and IT teams that want to check impersonation exposure, run controlled phishing simulations, and turn the results into in-person training and a management report.
* One allowlisting action by your IT team is required, and launch is subject to a security review of up to one business day.